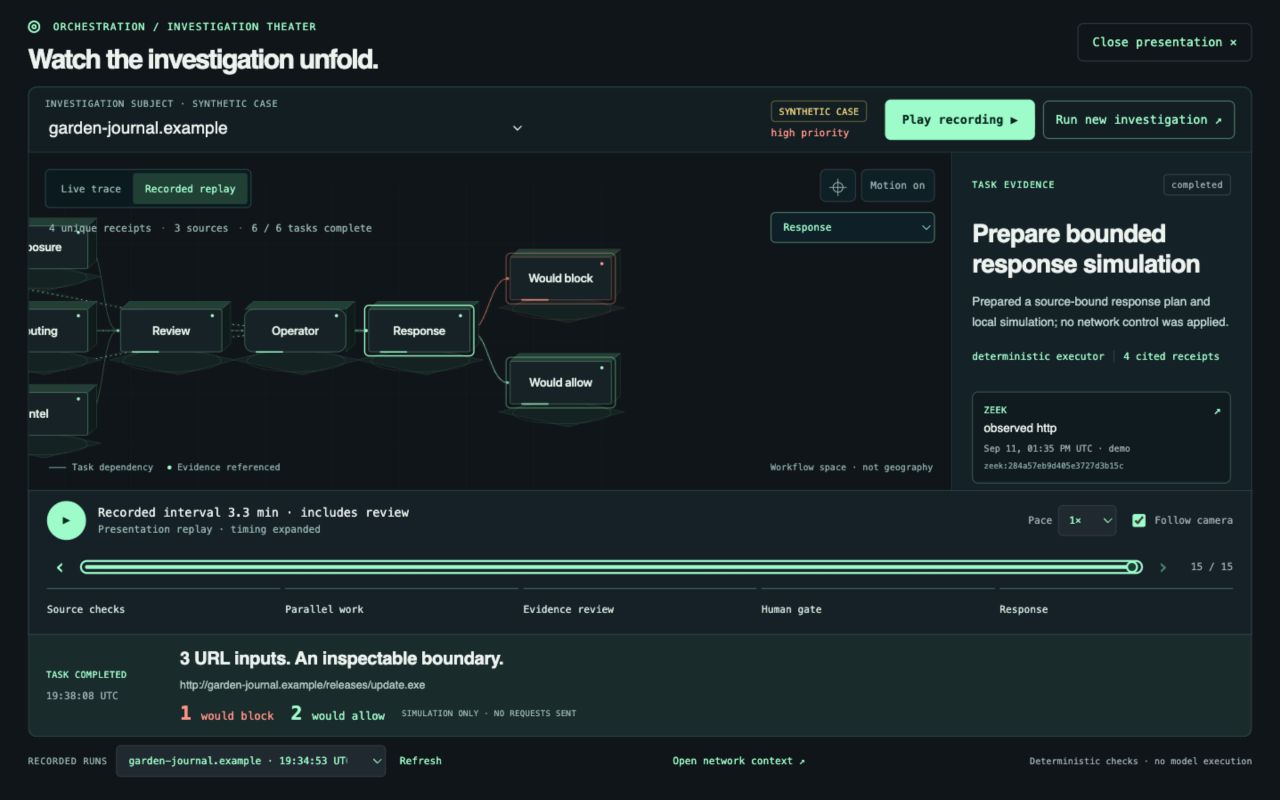
A defensive investigation workbench that connects what your assets actually did on the network to the evidence each source can actually establish. First-party exposure, routing history and packet evidence in one case, every claim traced to the one source that owns it, and every response held behind a human gate.
Security tooling blurs evidence together. A newly registered domain is treated as malicious because it is new. A correctly authorized route is treated as safe because it validates. Three feeds repeating one indicator are counted as three confirmations. Each shortcut produces a confident answer the evidence underneath cannot support.
Origin Observatory keeps those questions apart. Did a monitored asset touch this indicator? What changed in how its infrastructure is routed? Which source is entitled to say so? A stable, RPKI-valid route does not hide an exposure finding, a DNS query never becomes a claimed download, and overlapping reports are never added together as extra votes.
Eleven evidence roles, each with a single canonical source: NRD-db for discovery, Routinator for route authorization, Zeek for exposure, Arkime for packets, URLhaus for malware URLs, VirusTotal for reputation, Cloudflare Radar for network context. Overlap is recorded, never double-counted.
Exposure rules fire on what a monitored asset did, regardless of domain age or route validity. Routing rules fire on qualifying before-and-after transitions. Five explicit rules in all, and no blended score hiding which one fired.
Every routing comparison passes freshness and completeness gates: DNS, route and validator evidence within 24 hours, every stored address covered. Comparisons that fail are kept with the reason they were suppressed, not silently dropped.
The Arkime gateway splits metadata readers from packet readers. In isolated CI, 12 HTTP requests became 12 indexed sessions, one capture passed with matching digests through Arkime, the gateway and the Worker, and metadata-only users were denied packet access.
Durable investigations on the Cloudflare Agents SDK carry task receipts end to end. Response plans are bound to the evidence, the account and an expiry. No model can approve an action, and live enforcement is off by default.
Version 0.4 is a working detection and investigation prototype. Live precision, recall and false-positive rates have not been measured, and blocking in a connected account is not yet verified. The evaluation method to measure them is built in.
Origin Observatory is available to teams by request. Tell us about your sensors, the questions your analysts need answered and your access requirements, and we will scope an evaluation on your own data.
Request team access →